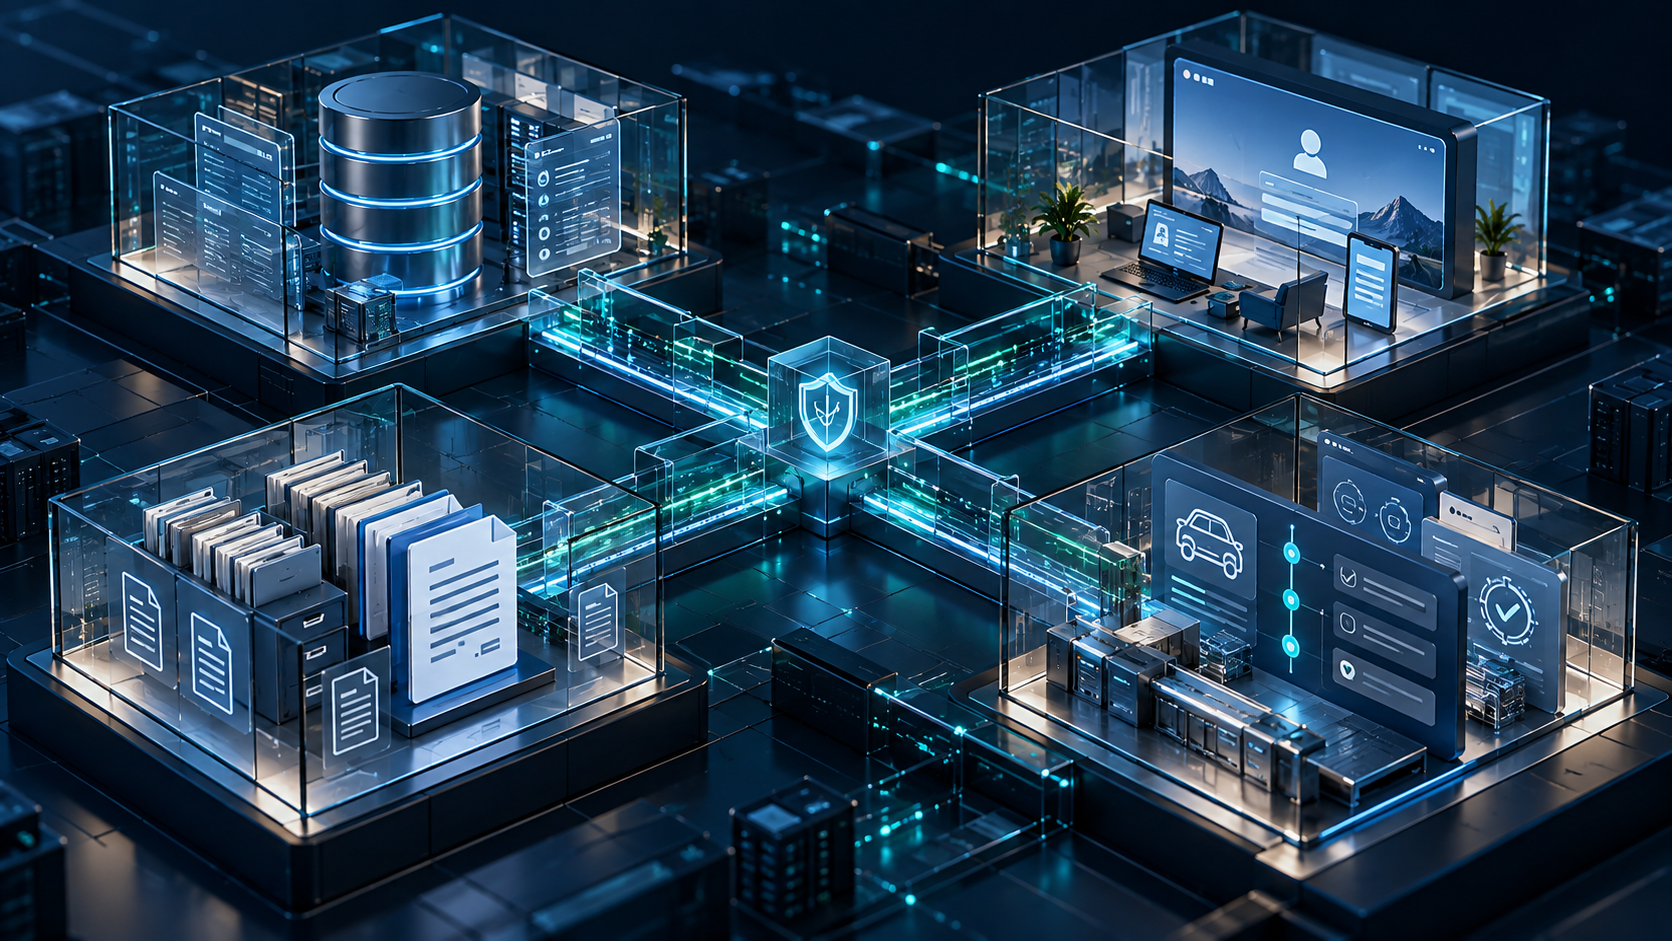
An AI claims tool rarely works in isolation. It receives material through a customer portal, checks coverage against policy records, interacts with claims history and sends work to employees. The quality of those connections can determine whether automation saves time or creates another layer of rework. An insurer should therefore treat integration and governance as part of the product design from the beginning.
The Digital Insurance Market report from KBV Research examines the solution and service layers supporting digital insurance. For organizations deploying AI in claims, that landscape translates into a practical architecture question: which system holds the authoritative record, and how does each downstream tool receive the right version of it?
A claim may begin with a form, a mobile photo, a repair invoice or a call-center note. Each item needs a stable case identifier, a receipt timestamp and a visible status. If a customer uploads a document twice because the portal gives no confirmation, the insurer may create duplicate work. If a file arrives but is not linked to the claim, an automated summary can look complete while omitting a decisive fact.
An intake design should validate file types, preserve originals and show what has been received. It should also make room for information that does not fit a standard field. A customer may need to explain timing, prior repairs or a special circumstance in their own words. The AI layer can help classify that material, but employees should be able to inspect the source when the case becomes consequential.
Coverage decisions depend on the applicable policy version, endorsements, dates and jurisdiction. A tool that pulls a generic product summary instead of the customer’s actual contract may draft a confident but wrong explanation. Integration should identify the authoritative policy record and retain a trace of the provision used in a recommendation. Claims history and service notes need similar care: they may provide context, but access should be limited to information needed for the task.
Data mapping is often less glamorous than a model demonstration. It is also where a deployment succeeds or fails. Teams should test cases with amended policies, missing attachments, multiple insured people and inconsistent document dates. A review queue must show an employee exactly which source generated a field and how to correct it. Without those details, a modern interface can simply make legacy data problems harder to see.
When a case is escalated, the reviewer should not have to reconstruct the claim across several screens. A useful workspace displays original evidence, policy references, earlier customer contact and the system’s suggested next step. It should make uncertainty visible and allow a person to override a recommendation with a recorded reason. That record can support quality review and later customer communication.
The review route also needs ownership. Define which team receives a flagged case, what priority it receives, and how a customer is updated while it waits. A backlog of exceptions can erase the speed gained from automated intake. Managers can monitor time to specialist, repeat requests for evidence and corrections after a decision. These measures connect system performance to customer experience.
The interface should distinguish observed facts from generated suggestions. A reviewer may see the date on an invoice, an extracted amount and a model summary; those should be traceable to the source. If a field is corrected, the change should be recorded and flow to downstream steps. Otherwise the same mistake can reappear in a customer letter or settlement calculation after an employee has already fixed it.
More connected systems create more points at which data access and operational resilience matter. In Europe, DORA has applied to relevant financial entities since January 2025, including insurance companies within its scope. Its existence is one reason for insurers to examine ICT risk and third-party dependencies as digital workflows expand. Requirements differ by entity and jurisdiction, so implementation should be assessed with the organization’s own obligations.
AI-specific governance also belongs in the change process. EIOPA’s 2025 opinion addresses insurance AI governance and risk management, while the IAIS application paper emphasizes existing supervisory expectations. Teams should test model changes against known claims examples, document revisions, monitor exceptions and retain a rollback plan. A small change in data extraction can have downstream effects on routing, review and customer letters.
Third-party contracts and internal responsibilities should make incident handling explicit. If a portal, model service or integration fails, claims staff need to know which information remains available and how to continue work. Testing a manual fallback may be less exciting than launching a new feature, but it protects continuity when a customer is already dealing with a loss.
Start with one administrative use where source documents and correction paths are clear. Measure accuracy and the work saved, then connect the output to a reviewer workspace. Expand to more consequential recommendations only after the handoff, evidence trace and customer explanation have been tested. Each stage should identify an accountable owner and a way to pause deployment when quality drops.
Digital insurance can improve claims service when the underlying systems agree on the facts and the people responsible can see how a recommendation was formed. The strongest architecture is one that keeps those conditions visible as the insurer scales.