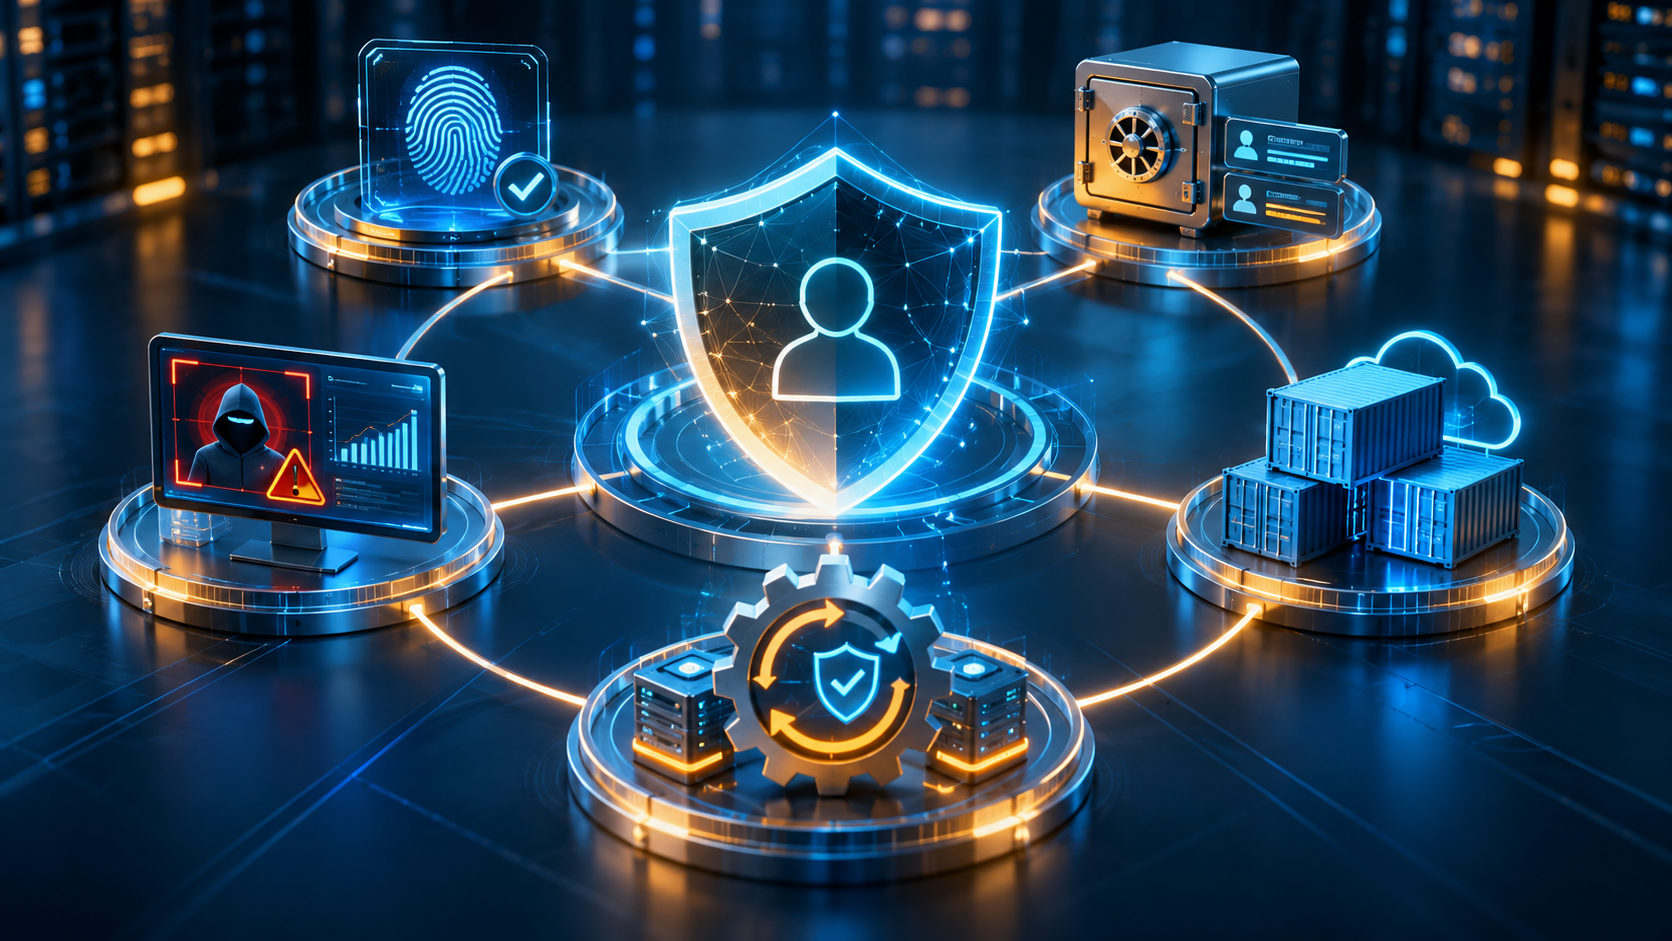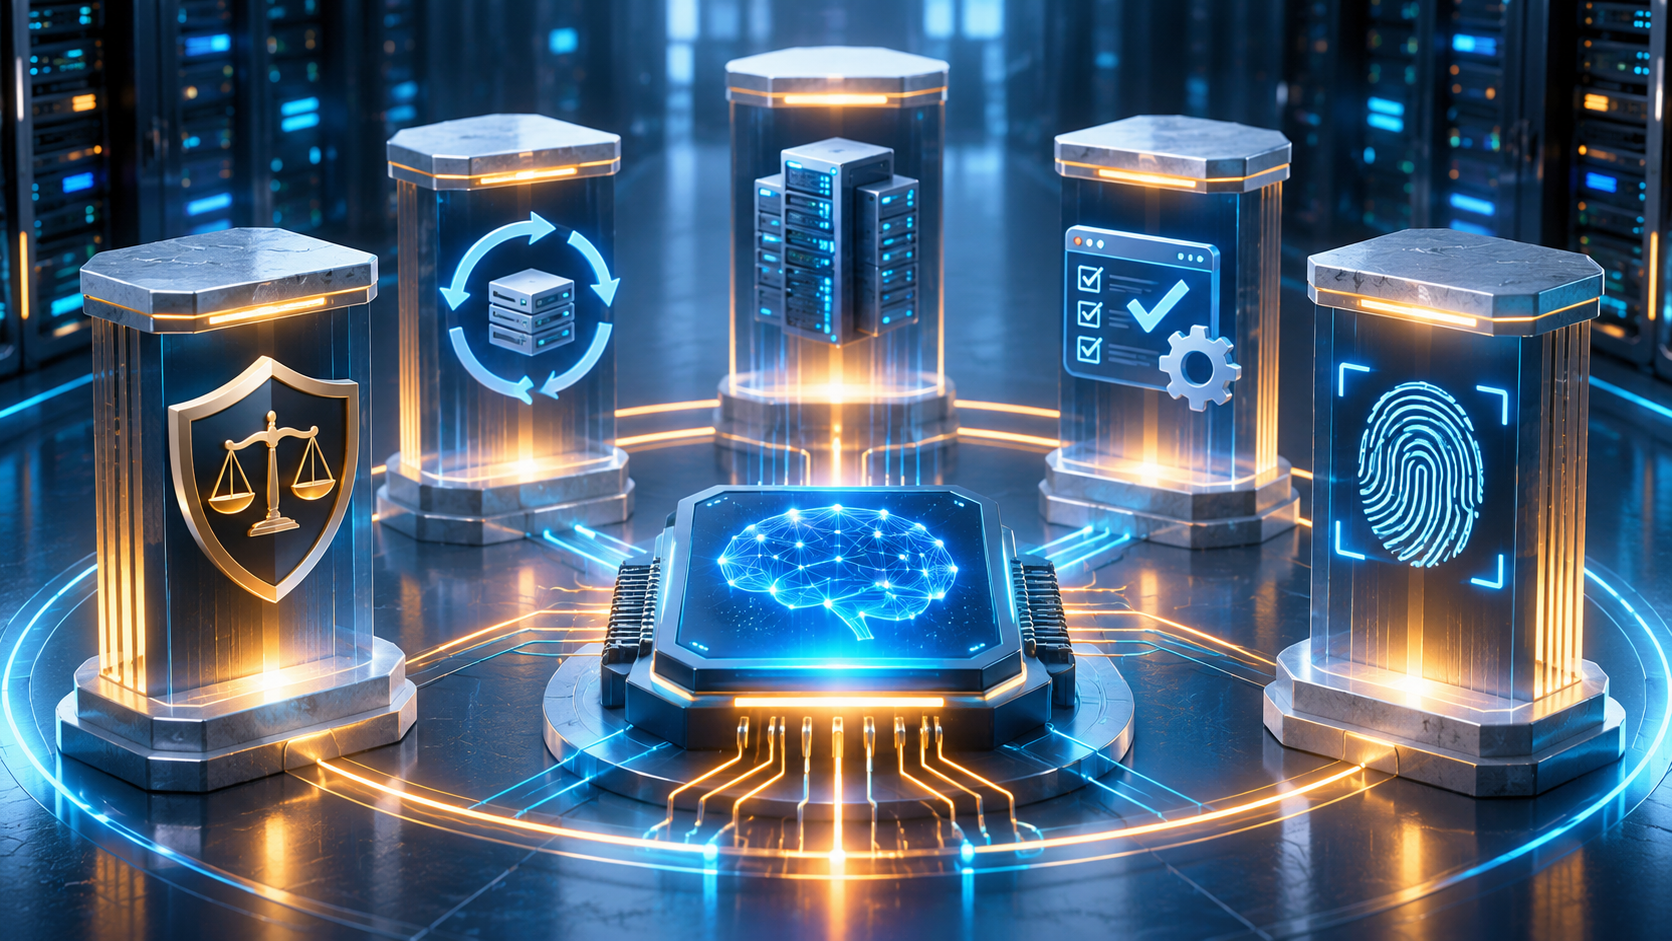
Five connected capabilities underpin dependable enterprise AI operations.
Enterprise AI readiness means being able to operate AI systems reliably, accountably and economically after a pilot ends. Five capabilities make that possible: governance, ModelOps, workload management, quality assurance and content provenance. A successful demonstration proves potential; it does not prove that an application can withstand changing data, real users or operational failures.
The foundations work as a system. Governance decides what is acceptable; ModelOps keeps models manageable; workload controls keep services available; testing checks whether outputs are fit for purpose; and provenance helps users understand how content was produced. The table below provides a quick implementation view.
|
Foundation |
Practical control |
|
Governance |
Named owner, risk tier and approval route |
|
ModelOps |
Versioned deployments and rollback criteria |
|
Workload management |
Capacity quotas, latency and cost targets |
|
Quality assurance |
Scenario tests and human review gates |
|
Provenance |
Origin records and traceable approvals |
AI governance begins with decisions that can be assigned to people. Each production use case needs an owner who defines its purpose, permitted data, intended users, escalation paths and conditions for stopping use. Compliance teams may set policy, but product and engineering teams must show how controls function in everyday operations. A model inventory should identify dependencies, third-party services and individuals authorized to approve material changes.
The AI governance market covers technologies and services associated with these oversight needs. A useful starting point is the NIST AI Risk Management Framework, which organizes risk work around governing, mapping, measuring and managing AI risks. A policy becomes meaningful when teams can demonstrate ownership, monitoring and documented decisions.
Models change in practice even when their underlying weights do not. Prompts evolve, data distributions shift and upstream applications introduce new inputs. ModelOps brings version control, release approvals, evaluation history, monitoring and retirement decisions into a manageable lifecycle. Teams should know which model version serves each application, how performance is assessed and what triggers a rollback.
For example, a customer-service assistant may require factuality checks, escalation rates and response-time monitoring, while a fraud model needs different performance and drift measures. The ModelOps market addresses the tooling that supports lifecycle coordination. The essential discipline is to treat every production model as a maintained service, not a finished experiment.
AI applications compete for finite computing resources. Batch analysis may tolerate queueing, while a customer-facing assistant needs predictable response times. Without priorities, teams can overprovision infrastructure or allow nonurgent jobs to affect critical services. Capacity quotas, scheduling policies, autoscaling and cost-per-task measurement help connect technical decisions to business needs.
The AI workload management market is relevant to these scheduling and allocation challenges. Organizations should compare workload types before buying more capacity: caching, smaller fit-for-purpose models, batch processing and demand forecasting may reduce cost without weakening service quality. Infrastructure efficiency matters only when the user experience and operating requirements are also met.
Conventional software tests check whether expected inputs produce expected outputs. AI systems can fail through plausible but inaccurate responses, ambiguous instructions, harmful edge cases and changing context. A strong test plan therefore includes representative user tasks, difficult inputs, security and privacy scenarios, and explicit thresholds for escalation to human review.
Automated tools can help generate tests and flag anomalies, a focus of the AI-powered software testing and QA market. Yet automated test generation is not independent assurance: a test generator can miss the same failure modes as the application. Release decisions should combine repeatable evaluations, documented acceptance criteria, regression testing and review of high-impact failures. The NIST Generative AI Profile offers additional risk considerations for generative systems.
Not by itself. Watermarking can provide a useful signal about AI-generated content, but transformations may weaken detection, and the absence of a watermark does not establish that material is human-made. Provenance is broader: it can include source records, editorial approvals, creation tools, timestamps and content credentials where supported. The right evidence depends on the business use case.
The AI watermarking market examines one part of this emerging toolset. For a publishing workflow, retaining original assets and approval records may be as important as applying a watermark. Teams should describe precisely what a provenance signal supports and avoid treating any single detection result as conclusive proof.
Begin with one production application rather than a company-wide technology purchase. Name its owner, document intended users and data, set quality and service targets, record the deployed model version and test foreseeable failures. Then define who receives alerts, who can pause the service and how evidence is preserved after an incident. The NIST AI RMF Playbook offers practical actions teams can adapt to their circumstances.
A useful readiness review asks five questions: Who is accountable? What changed since approval? Can capacity meet demand? What evidence supports output quality? Can the organization explain where important content came from? If these answers are clear and testable, expansion becomes a managed decision rather than a leap of faith.
Enterprise AI readiness is not a single platform or certification. It is the ability to connect ownership, model operations, computing resources, testing and provenance into a repeatable operating model. Organizations that establish these controls early are better positioned to scale useful AI applications while recognizing and responding to their limits.